Case study
Notamperdata
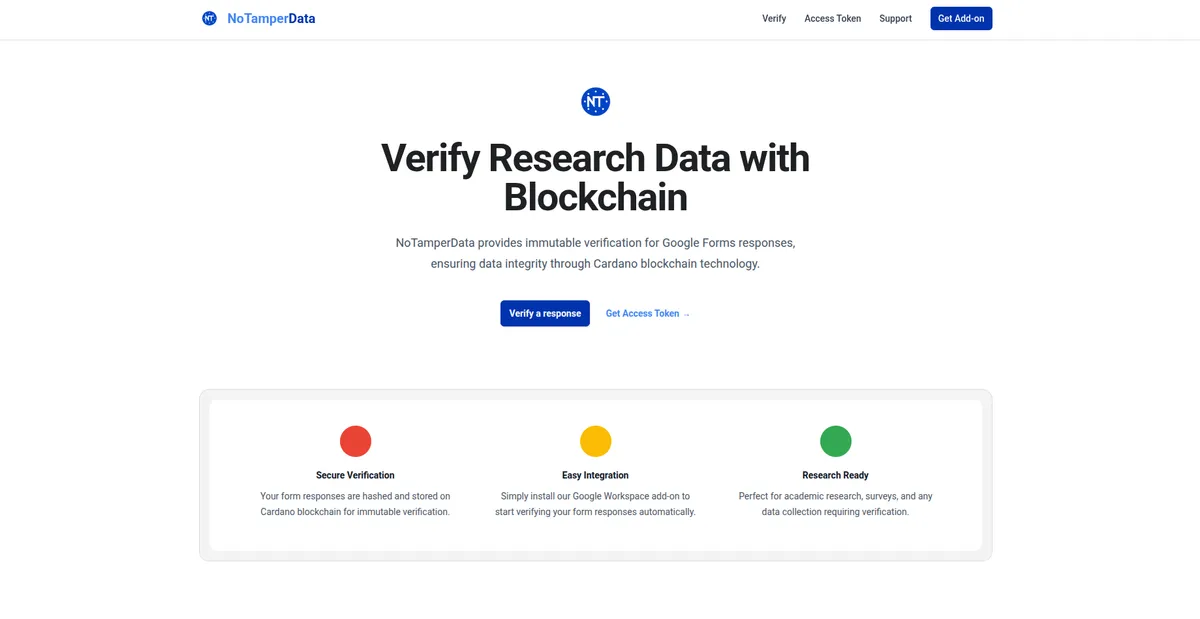
A tamper-evident audit trail for research data, published on the Google Workspace Marketplace and maintained for two years, where only a hash ever leaves Google's infrastructure.
- Role
- Lead Developer & Maintainer
- Dates
- Mar 2024 – Feb 2026
- Links
- Stack
- Google Apps Script
- Next.js
- TypeScript
- Cardano
- Aiken
- GCP
The problem
Research data collected through Google Forms has no built-in integrity guarantee. Responses can be edited or deleted between collection and analysis, and no one else can check that the data a researcher presents is what they collected.
Existing options pull the data out of Google's ecosystem or route it through a third party. The constraint was integrity checks without the data leaving Google's infrastructure.
What I built
- An open-source Google Workspace add-on, published on the Workspace Marketplace, that hashes each form response with SHA-256.
- A Next.js verification app that anchors each hash on the Cardano blockchain and lets anyone re-hash a response and check it against the on-chain record.
- Two years of maintenance as lead developer, from March 2024 to February 2026.
How it works
Key decisions
Store only the hash
Instead ofStoring the responses themselves, on-chain or on a server
A SHA-256 hash identifies the data without revealing it, and any change to a response breaks the match. The responses stay in the researcher's Google account under their own access controls; the chain holds only the proof.
A Workspace add-on, not a separate service
Instead ofCloud Functions that each researcher configures
Apps Script is Google Workspace's own extension mechanism: it reads Forms and Sheets directly and installs from the Marketplace in one click. For researchers who aren't developers, that matters more than Apps Script's runtime limits.
Results
Published on the Google Workspace Marketplace and maintained as open source for two years, with a privacy guarantee that comes from the design: the data never leaves Google.
Screenshots